Security Assessments
You want to know exactly where your security gaps are before an attacker, a regulator or your board finds them for you.
Why Sparkhound for Your Next Security Risk Assessment
We Scope Before We Scan
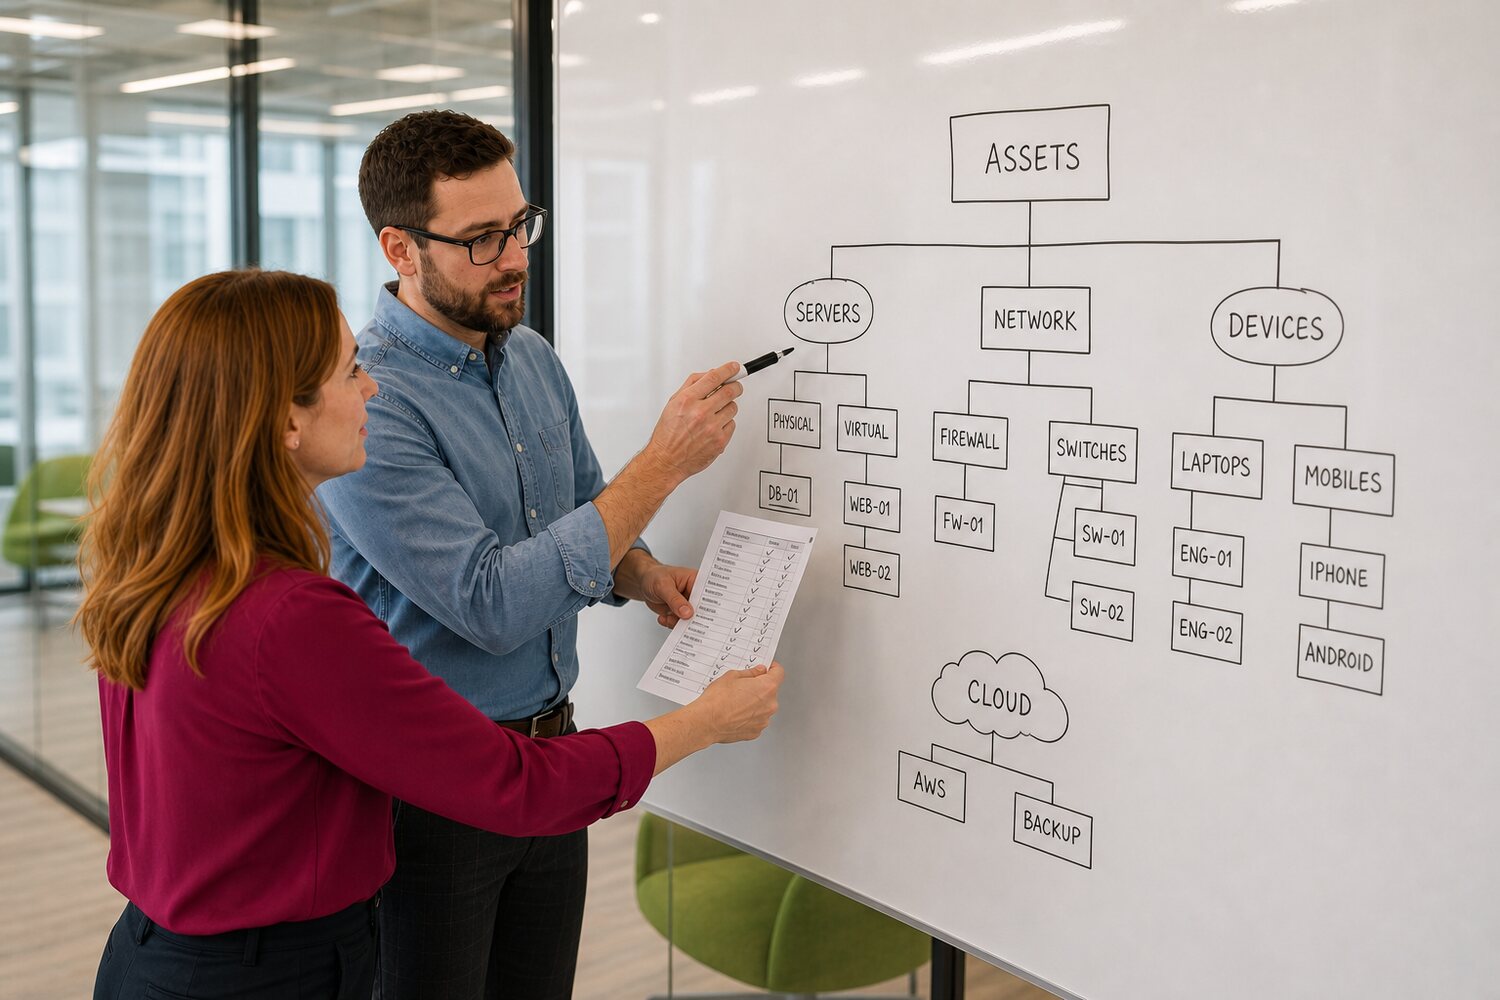
We build a full asset inventory first, then recommend tools and testing. Skipping that step is how assessments miss real risk.
Findings Map to a Framework, Not Just a List
Every result ties to NIST CSF, CIS Controls, or Microsoft Secure Score. You leave with a maturity view and a prioritized roadmap, not a pile of raw findings.
We Stay With You After the Report
An assessment is the start of the relationship, not the end of it. Findings can roll directly into remediation, managed security, or a formal compliance program.
How We Help
Vulnerability Assessment Services
A systematic scan of networks, systems, and applications that identifies missing patches, misconfigurations, and outdated software.
Penetration Testing Services
Simulated attacker behavior used to test whether discovered weaknesses can be exploited and what the real business impact could be.
Security Risk Assessments
Asset inventory, threat modeling, and business-impact analysis benchmarked against your actual environment, not a generic checklist.
Compliance Audits
Controls evaluated against HIPAA, PCI DSS, CMMC, SOC 2, or applicable state privacy requirements, with documentation to show where you meet the standard and where work remains.
Security Posture and Maturity Reviews
A framework-based review across governance, identity, protection, detection, response, and recovery, followed by a prioritized roadmap.
Microsoft Secure Score Reviews
A low-friction starting point for organizations running Microsoft 365, aligned to NIST CSF, NIST SP 800-171, and CIS Controls.
Security Risk Assessment for Your Tech Stack
How We Work
Scope the Engagement
We define the systems, IP ranges, domains, applications, APIs, and cloud environments in scope. We also document what is excluded before testing begins.
Build the Asset Inventory and Gather Documentation
A cross-functional team collects security policies, system configurations, and prior audit reports. Complete asset visibility comes first because incomplete visibility creates blind spots.
Test and Prioritize Findings
We rank findings by exploitability, active threat intelligence, and business impact, not raw severity scores alone, so you receive a ranked remediation queue with clear ownership.
Recommend the Next Step
Every engagement ends with a practical recommendation: targeted remediation, ongoing managed security, or a formal compliance program. We also recommend a testing cadence based on your risk level.
What Our Clients Say
We needed a flexible partner who could respond and adapt to our needs. Sparkhound has exceeded our expectations every step of the way.
Eric Abrams, IT Manager, Noble Energy
Ready to Find Out Where You Stand?
Book a Security Assessment ConsultationFrequently Asked Questions About Security Risk Assessment
What Is a Security Risk Assessment?
A security risk assessment is a structured evaluation of your technology environment, policies, and practices that identifies weaknesses before attackers do. It combines asset inventory, threat modeling, vulnerability identification, and business-impact analysis to show the gaps your organization needs to address.
What Is an Information Security Risk Assessment?
An information security risk assessment focuses on how information is stored, accessed, and protected. It provides the documented review that banks, insurers, regulators, and customers may request when a verbal assurance is not enough.
How Much Does a Security Risk Assessment Cost?
Security risk assessment cost depends on the size and complexity of your environment, the number of systems in scope, and whether the engagement includes hands-on penetration testing. Sparkhound scopes the asset inventory, testing requirements, and expected deliverables before pricing the work.
How Often Should Risk Assessments Be Conducted?
Most organizations should conduct a full risk assessment at least annually and after a major change, such as a cloud migration, acquisition, new regulated-data environment, or new regulatory obligation. Higher-risk systems may also need more frequent vulnerability scanning or targeted testing.
How Do You Perform a Cybersecurity Risk Assessment?
A cybersecurity risk assessment begins by defining the systems, applications, cloud environments, and data in scope. It then moves through asset inventory, documentation review, vulnerability and threat testing, and prioritization based on exploitability and business impact. The result is a ranked remediation plan with ownership and next steps.
What’s the Difference Between a Vulnerability Scan, a Penetration Test, and a Risk Assessment?
A vulnerability scan identifies known weaknesses. A penetration test attempts to exploit selected weaknesses to demonstrate real-world impact. A risk assessment goes broader by combining those technical findings with asset inventory, threat modeling, and business-impact analysis to help determine what to fix first.
What Happens After a Security Assessment Is Complete?
After the assessment, you receive a written report of findings ranked by exploitability and business impact. The report can include a maturity score against a framework such as NIST CSF or CIS Controls, along with recommendations for remediation, managed security, or a compliance program.
Do I Need a Penetration Test if I Already Run Vulnerability Scans?
Often, yes. Vulnerability scans find known weaknesses but do not show whether an attacker can exploit them or the resulting business impact. Penetration testing provides that validation and helps your team prioritize remediation.